What does DDoS mean?
DDoS stands for Distributed Denial of Service. The goal is not to steal data. The goal is to make a service unavailable to the people who need it by overwhelming it with more traffic or requests than it can handle.
The word “distributed” is the key. The traffic does not come from one source. It comes from many devices at the same time, which makes it much harder to block.
DoS vs DDoS: what is the difference?
A DoS (denial of service) attack comes from a single source, such as one computer. It is easier to spot and block, because you can simply stop traffic from that source.
A DDoS attack comes from many sources at once, often thousands. Blocking one source does not help, because the traffic keeps arriving from everywhere else.
How does a DDoS attack work?
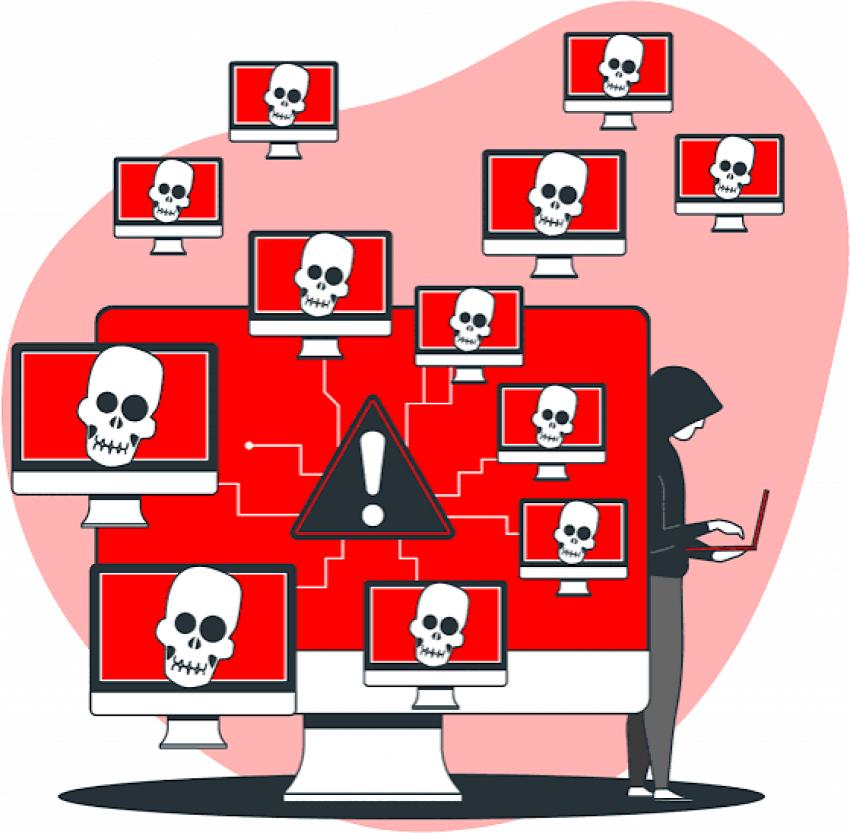
Most DDoS attacks use a botnet. A botnet is a network of devices, such as computers, servers, routers, cameras and other connected gadgets, that have been infected with malware and can be controlled remotely, usually without their owners knowing.
An attacker follows a simple pattern:
The attacker infects many devices and links them into a botnet.
The attacker chooses a target, such as a website or server.
The attacker commands all the devices to send traffic or requests to the target at once.
The target becomes overloaded, slows down or stops responding to real users.
Some attackers also rent botnets from criminal services instead of building their own. Launching a DDoS attack on a system you do not own is illegal in most countries.
The main types of DDoS attacks
Volumetric attacks
These try to fill up the target’s internet connection with huge amounts of traffic, like clogging a motorway so no cars can pass. Examples include UDP floods and DNS amplification attacks, where small requests are tricked into producing much larger responses aimed at the victim.
Protocol attacks
These exploit weaknesses in how network connections are set up, using up the resources of servers, firewalls or load balancers. A well-known example is the SYN flood, which sends many connection requests and never completes them, leaving the server waiting.
Application-layer attacks
These target the website or application itself, using requests that look like normal user activity, such as loading a page or submitting a search again and again. An HTTP flood is a common example. They can be harder to spot because each request looks harmless on its own, and they can cause problems even with smaller amounts of traffic.
Signs you might be under a DDoS attack
Your website or app becomes very slow or unreachable.
You see a sudden, unexplained spike in traffic, often from unusual locations or in strange patterns.
Many requests target the same page or endpoint.
Your internet connection or network slows to a crawl.
Servers show high usage even though you have not had a real increase in customers.
Keep in mind that a legitimate surge, such as a viral post or a sale, can look similar. Looking at where the traffic comes from and what it does helps tell the difference.
Why do attackers use DDoS?
Motives vary:
Extortion, where attackers demand payment to stop an attack
Disruption of a competitor or an online service
Activism or protest
Revenge or personal grudges
A distraction, to keep a security team busy while another attack takes place
Showing off, or testing tools
What damage can a DDoS attack cause?
Downtime and lost sales, especially for online shops and booking services
Frustrated customers and a damaged reputation
Extra costs for emergency support, extra bandwidth or cloud resources
Lost productivity, as staff stop work to deal with the problem
In some cases, broader risk, if the attack is used as cover for something else
Who is at risk?
Any organization with an online presence can be targeted, from small shops to large platforms. Online stores, banks, gaming services, media sites, schools, hospitals and public services are common targets, but smaller sites are not immune. Many attacks are automated and aimed at whatever is reachable.
How to protect against DDoS attacks
No single measure stops every attack, but a combination makes a big difference.
Use a DDoS protection or content delivery service. These services spread traffic across large networks and filter out malicious requests before they reach your servers.
Add a web application firewall. It can block suspicious requests aimed at your application.
Set rate limits. Limiting how many requests one source can make reduces the effect of repeated requests.
Plan for extra capacity. Cloud platforms that scale automatically, and enough bandwidth, give you breathing room.
Keep systems updated and secure. Updated software and strong passwords make your own devices less likely to be recruited into a botnet.
Know your normal traffic. Monitoring tools that show your usual patterns help you spot trouble early.
Talk to your hosting provider or internet provider. Many offer protection or can help during an attack, so know your options before you need them.
Have a response plan. Decide in advance who to call, what to switch off, how to inform customers and how to switch to backup systems.
What to do if you are under attack
Confirm that it is an attack, not a normal traffic spike.
Contact your hosting provider, security provider or internet provider immediately.
Turn on any protection you have, such as filtering or a special mitigation mode.
Keep logs and notes about what happened and when.
Keep customers informed with simple, honest updates.
After the attack, review what worked, what did not, and how to improve.
Conclusion
A DDoS attack is an attempt to knock a service offline by flooding it with traffic from many sources. It does not usually steal data, but it can cost a business money, customers and trust. Understanding how these attacks work, watching for early signs and having protection and a response plan in place will make you much better prepared. Start with the basics: know your normal traffic, use a trusted protection service and decide in advance what you will do if it happens.